PCI DSS Insights
Expert guidance on PCI DSS compliance, security best practices, and industry updates.
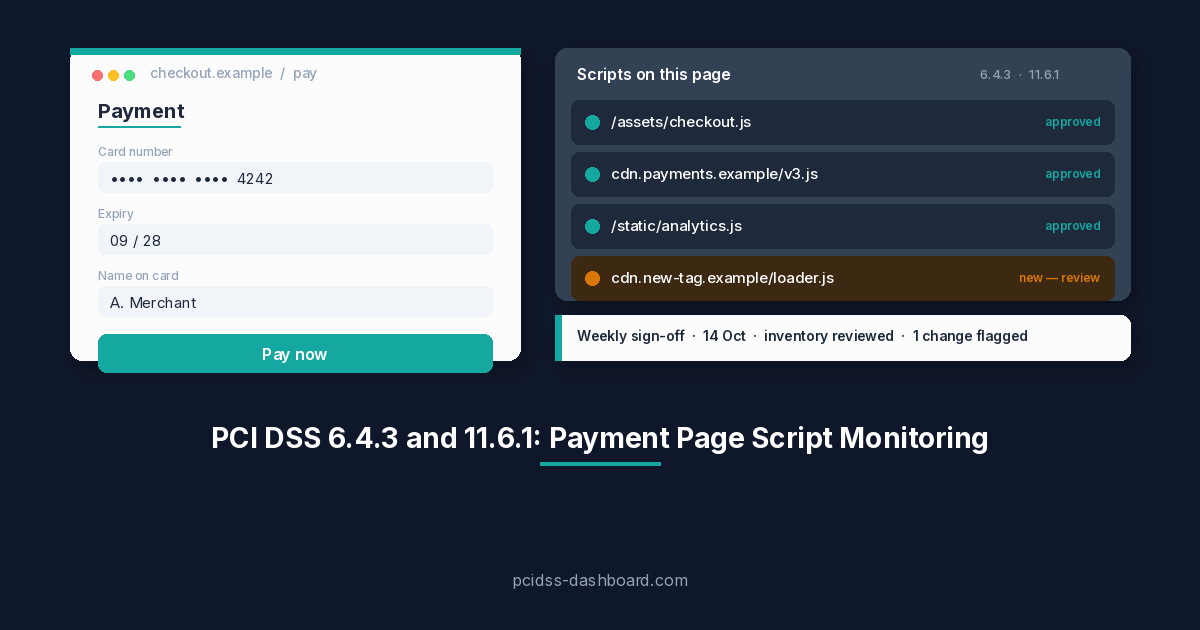
PCI DSS 6.4.3 and 11.6.1: Payment Page Script Monitoring
PCI DSS v4.0.1 6.4.3 asks you to authorise, inventory and justify every payment page script; 11.6.1 asks for weekly detection …
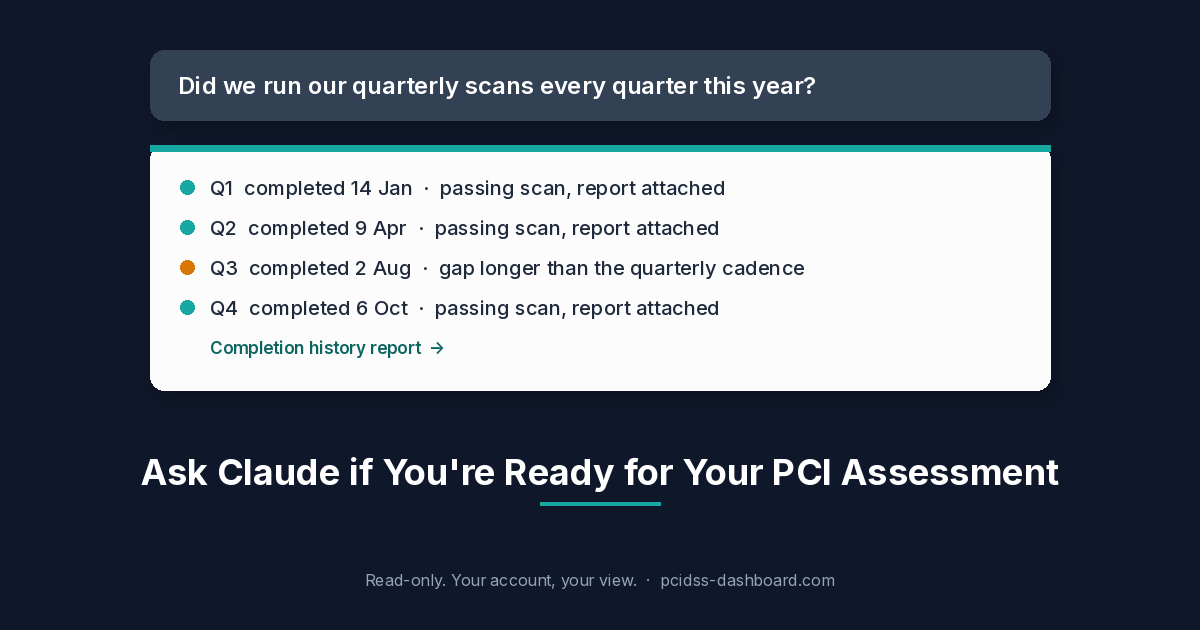
Ask Claude if You're Ready for Your PCI Assessment
Your assessor asks for twelve months of quarterly scan evidence. Now you can ask Claude the same question and get …
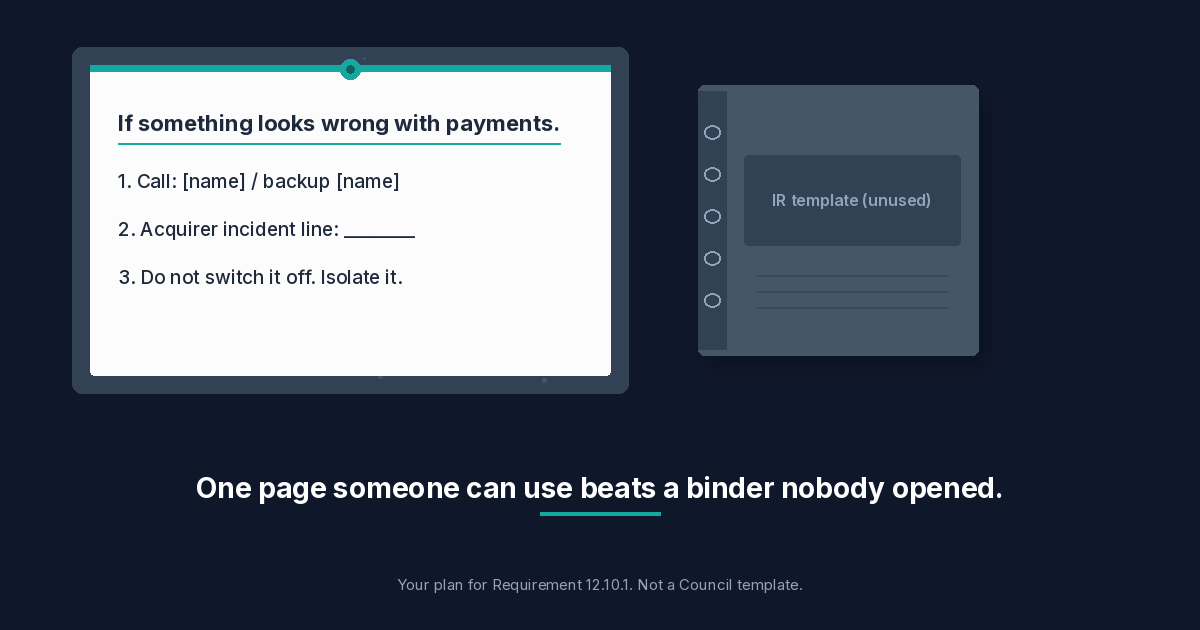
PCI DSS 12.10.1: The Incident Response Plan Your SAQ Asks For
Requirement 12.10.1 asks for a plan that is ready to activate, not a template nobody opened. What each v4.0.1 SAQ …
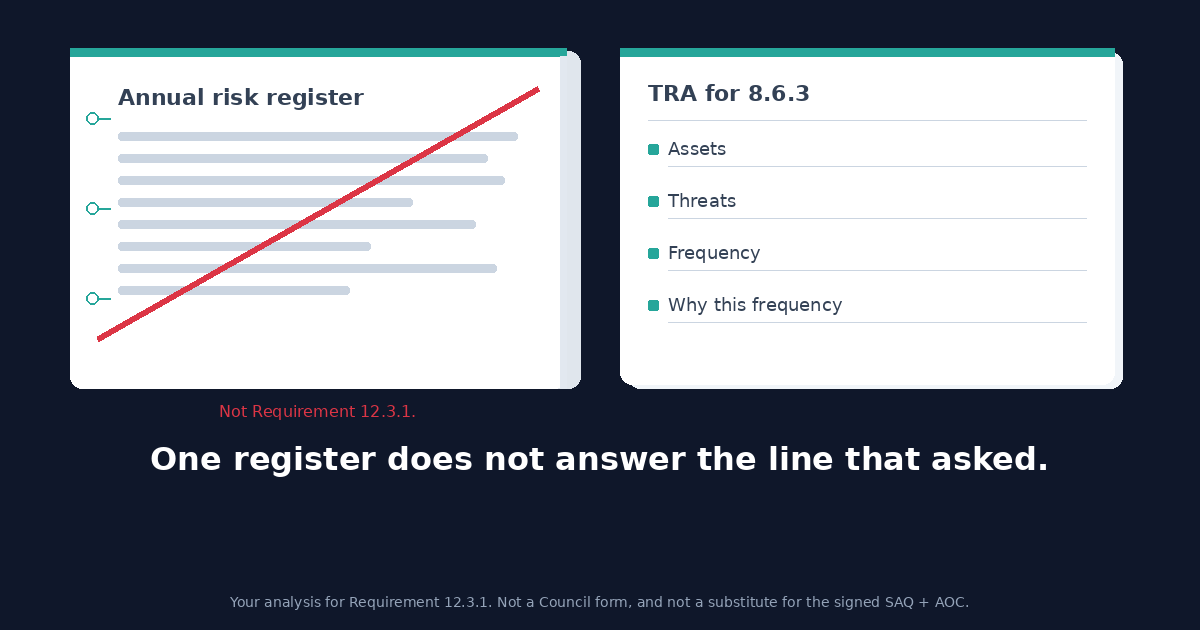
Targeted Risk Analysis: Requirement 12.3.1 Is Not Your Risk Register
Requirement 12.3.1 is not a company risk assessment. In PCI DSS v4.0.1 it is one documented analysis for each requirement …
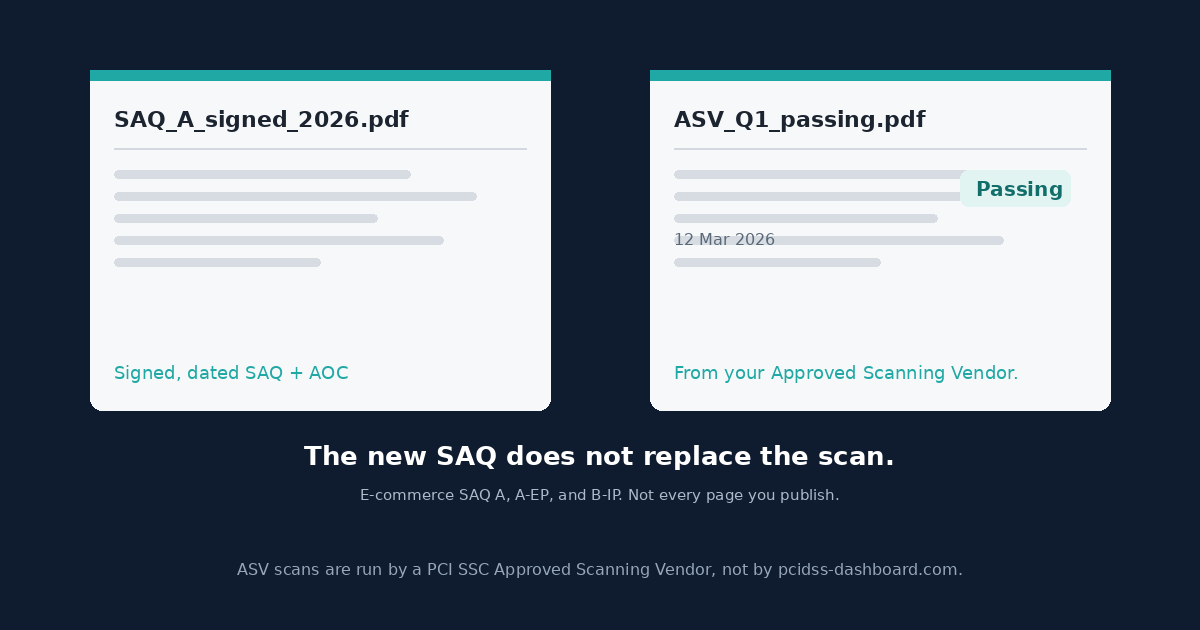
Quarterly ASV Scans: Why a Fresh SAQ Still Bounces
Requirement 11.3.2 is a passing quarterly ASV scan, not a line you tick because the SAQ PDF is new. Where …
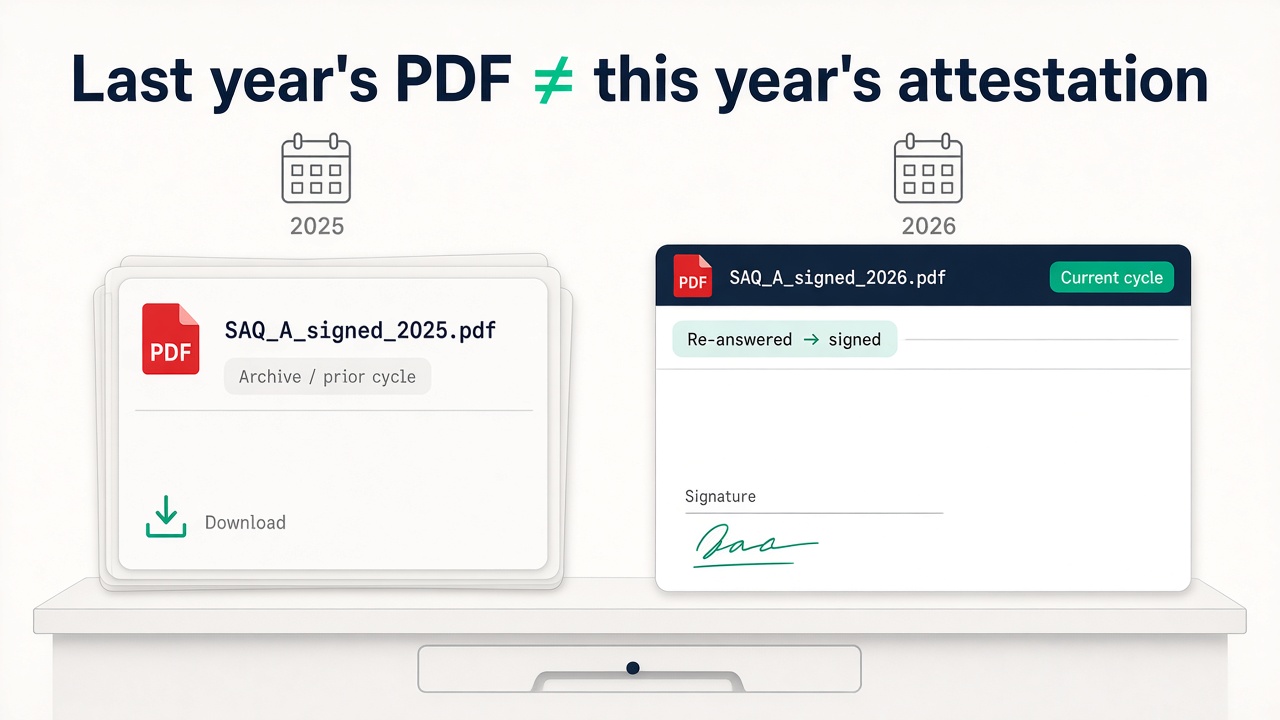
SAQ Renewal: Last Year's Signed PDF vs This Year's Cycle
Last year's signed SAQ PDF is an archive artefact, not this year's attestation. Prior-cycle PDFs stay downloadable; a new cycle …
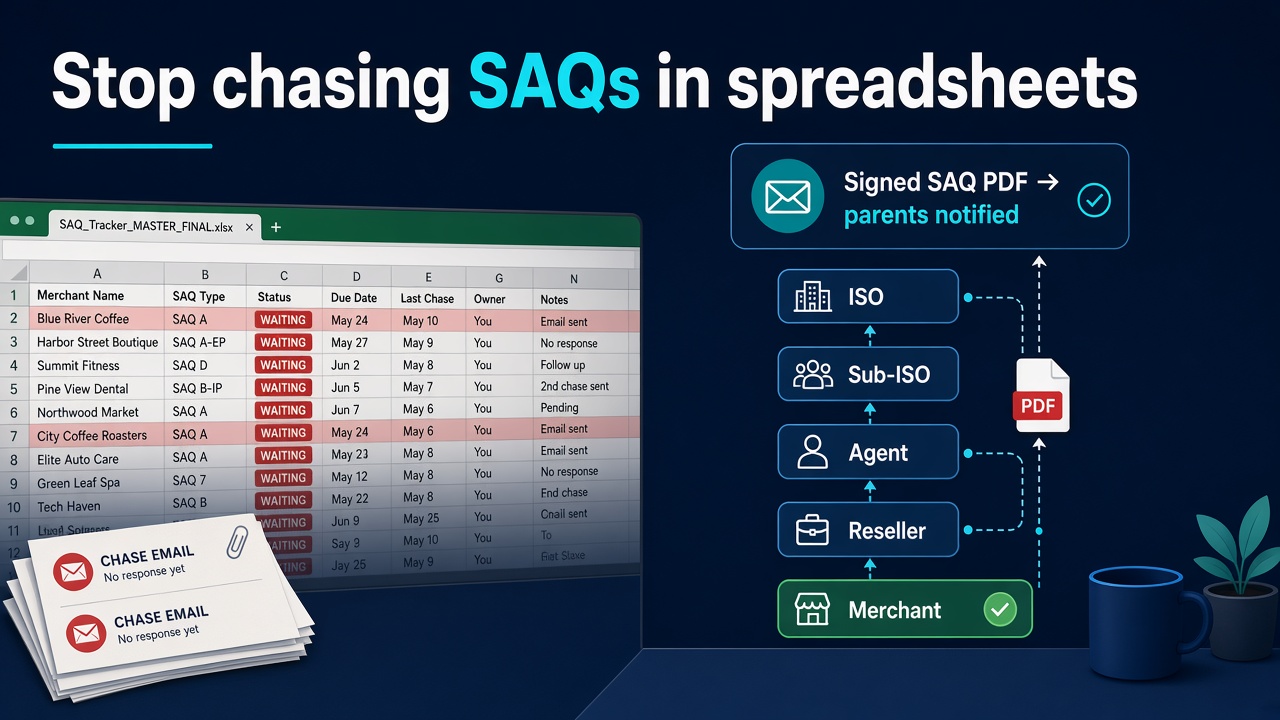
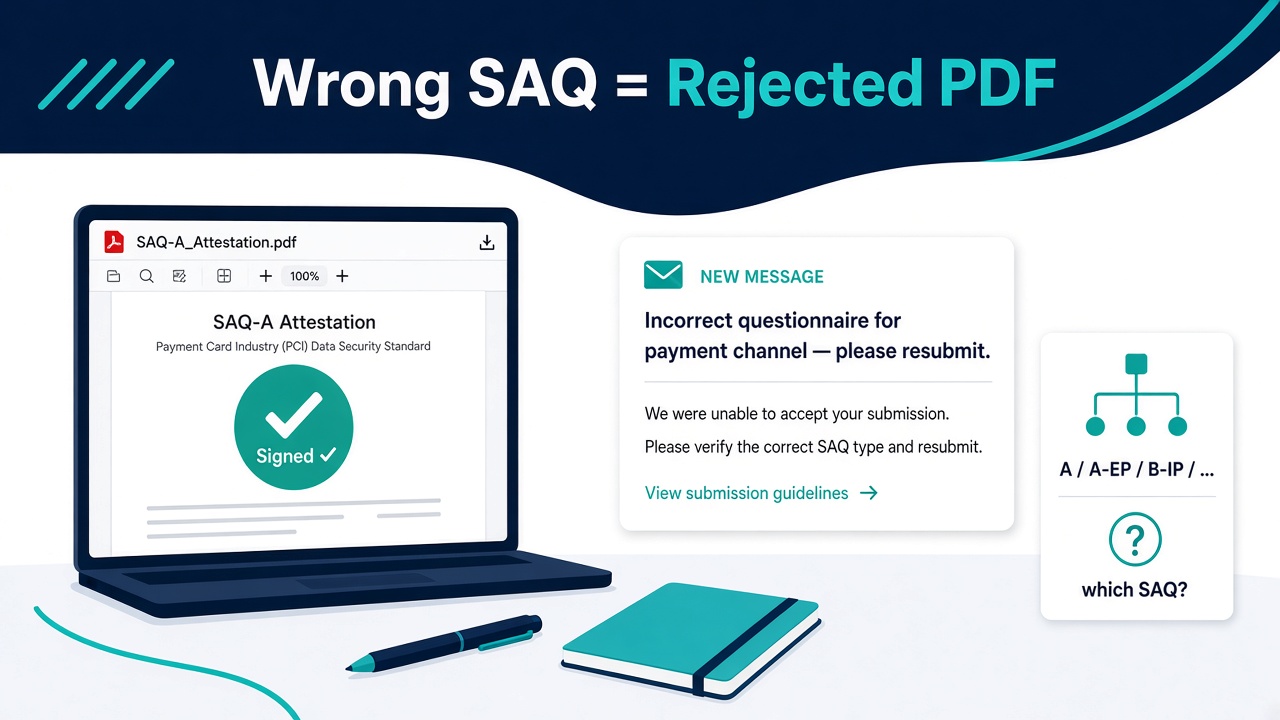
What Your Acquirer Actually Wants (Hint: Not Another Dashboard Login)
Your bank isn't asking for a green compliance score. They want a signed, dated SAQ/AOC package. Here's what to hand …
PCI DSS Requirement 12.8: Your Payment Vendor Being "Compliant" Doesn't Mean You Are
Requirement 12.8 is the TPSP control most SAQ A merchants half-do. Inventory, contracts, due diligence, annual checks — and why …